Cybersecurity has become one of the most important areas of technology, and organizations need professionals who can find weaknesses before real attackers exploit them. Penetration testing is one of the most practical career paths for people who enjoy ethical hacking, problem-solving, networking, programming, and security research.
If you are considering a career in offensive security, Pen Testing Jobs can lead to roles involving networks, web applications, cloud platforms, wireless systems, APIs, and enterprise environments. The work is not simply about running hacking tools. Professional penetration testers must understand how systems work, identify realistic attack paths, document evidence, communicate risks, and help organizations fix security weaknesses.
The U.S. Bureau of Labor Statistics projects employment of information security analysts to grow by 21% from 2025 to 2035, with about 14,100 openings per year on average. The median annual wage for information security analysts was $129,180 in May 2025. Penetration testing is a specialized cybersecurity occupation, so these figures should be treated as broader cybersecurity-market indicators rather than a specific penetration-tester salary.
What Does a Penetration Tester Do?
A penetration tester, often called a pentester, performs authorized security testing to discover vulnerabilities in systems and determine how those weaknesses could potentially be exploited.
The goal is not to damage a company’s systems. Instead, the tester works within an agreed scope and uses controlled attack techniques to provide evidence of security weaknesses.
The U.S. Department of Labor’s O*NET OnLine classifies penetration testers as a distinct occupation and describes their work as evaluating network security through simulated internal and external cyberattacks. The occupation is currently listed as a “Bright Outlook” occupation and was updated in 2026.
Typical responsibilities include:
- Planning penetration tests
- Reviewing the testing scope and rules of engagement
- Performing reconnaissance and information gathering
- Identifying vulnerabilities
- Testing networks, applications, and systems
- Attempting controlled exploitation
- Evaluating privilege escalation opportunities
- Testing security controls
- Documenting evidence and technical findings
- Preparing professional security reports
- Explaining vulnerabilities to technical and nontechnical stakeholders
- Recommending appropriate remediation measures
O*NET specifically lists tasks such as documenting penetration-test findings, identifying security weaknesses, writing audit reports, gathering cyber intelligence, tracking hacking trends, and developing tests that simulate techniques used by threat actors.
Types of Pen Testing Jobs to Consider
Penetration testing is broader than a single job title. Employers use different titles depending on the environment being tested, the customer’s requirements, and the tester’s experience.
1. Junior Penetration Tester
Junior roles are often an entry point for people building professional experience in offensive security.
A junior tester may work under senior team members while performing vulnerability validation, reconnaissance, basic exploitation, evidence collection, documentation, and other portions of an assessment.
Current job listings demonstrate that junior opportunities exist across different environments. For example, a current ClearanceJobs listing for a Junior Penetration Tester involves assessments covering web applications, infrastructure, cloud environments, and related technologies.
This type of position can be useful for developing real-world testing experience while learning professional reporting and client communication.
2. Network Penetration Tester
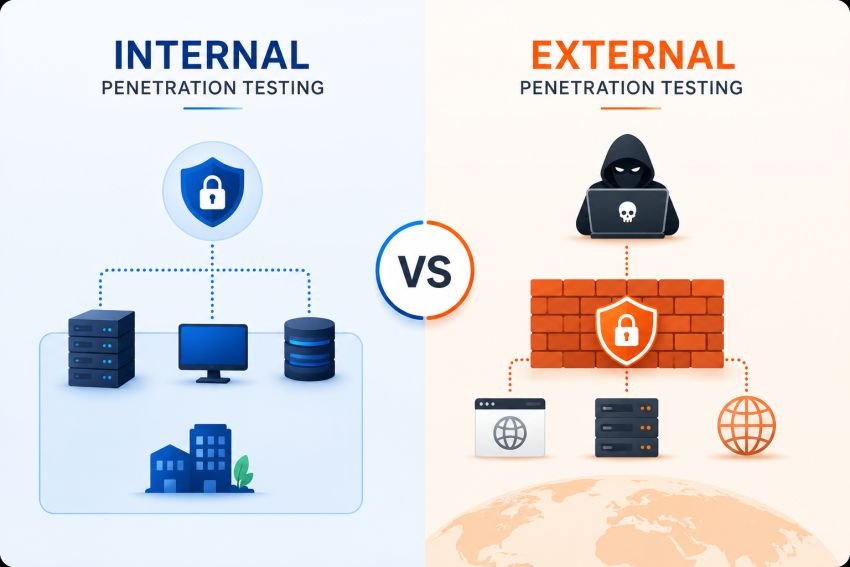
Network pentesters assess internal and external network environments.
Their work can include examining:
- Network services
- Firewalls
- VPN configurations
- Remote access systems
- Servers
- Active Directory environments
- Network segmentation
- Authentication mechanisms
- Exposed infrastructure
Current remote listings also show employers looking for testers who can assess internet-facing assets such as web applications, firewalls, VPN/RDP services, and other externally accessible systems.
3. Web Application Penetration Tester
Web application testers focus on applications and APIs.
They investigate issues involving authentication, authorization, input validation, session management, business logic, APIs, and other application-security weaknesses.
Knowledge of HTTP, JavaScript, databases, web architecture, and common application vulnerabilities can be particularly useful for this career path.
4. Cloud Penetration Tester
As organizations increasingly use cloud infrastructure, security testing has expanded beyond traditional networks.
Cloud-focused testers may assess:
- Identity and access management
- Cloud configurations
- Storage permissions
- Network controls
- Serverless components
- Containers
- APIs
- Cloud applications
- Authentication and authorization
O*NET’s current employer-posting data shows AWS and Azure among the technologies appearing in penetration-tester job postings.
5. Red Team Operator
Red team roles generally involve broader adversary simulations designed to test an organization’s ability to prevent, detect, and respond to realistic attacks.
Depending on the engagement, a red team may combine network exploitation, social engineering, physical security testing, application weaknesses, credential attacks, and other authorized techniques.
These roles normally require stronger practical experience than basic junior penetration-testing positions.
6. Senior Penetration Tester
Senior testers typically take greater responsibility for planning assessments, selecting methodologies, reviewing findings, mentoring junior testers, communicating with customers, and handling complex environments.
Current job listings illustrate this progression. ClearanceJobs currently displays senior penetration-testing roles involving independent testing of applications, systems, and enclaves, while some listings require several years of experience and security clearances.
Penetration Testing Career Path
There is no single route into penetration testing. Some professionals start with networking or systems administration, while others enter through software development, security operations, vulnerability management, or cybersecurity education.
A typical progression might look like this:
| Career Stage | Common Focus | Skills to Build |
|---|---|---|
| Beginner | IT and security fundamentals | Networking, Linux, Windows |
| Junior Tester | Basic security assessments | Reconnaissance, scanning, vulnerability validation |
| Penetration Tester | Independent assessments | Exploitation, reporting, web/network testing |
| Senior Tester | Complex engagements | Advanced exploitation, cloud, Active Directory |
| Red Team Specialist | Adversary simulation | Attack chains, evasion, operations |
| Security Consultant | Client-focused security work | Testing, reporting, risk communication |
| Offensive Security Lead | Team and assessment leadership | Strategy, architecture, mentoring |
The path is not necessarily linear. Someone with strong development experience may move toward application security, while a network administrator may transition into infrastructure penetration testing.
Skills Employers Look for in Pentesters
Technical knowledge is essential, but successful testers also need communication and analytical skills.
Networking Fundamentals
A strong understanding of networking is one of the foundations of penetration testing.
You should understand concepts such as:
- TCP/IP
- DNS
- HTTP and HTTPS
- Routing
- Ports and protocols
- VPNs
- Firewalls
- Network segmentation
- Authentication
- Active Directory
Without understanding how a system works, security tools can become little more than buttons to click.
Linux and Windows
Penetration testers commonly work across Linux and Windows environments.
Linux knowledge is particularly useful for security tooling and command-line workflows, while Windows and Active Directory knowledge is important for assessing many enterprise environments.
O*NET’s 2025 employer-posting data identifies Linux, PowerShell, AWS, Azure, Active Directory, and Kali Linux among technologies appearing in penetration-tester postings.
Programming and Scripting
You do not necessarily need to become a full-time software developer, but programming can significantly improve your effectiveness.
Python is particularly valuable for automation, data processing, custom tooling, and security research.
Current O*NET job-posting data lists Python in 30% of penetration-tester postings in its 2025 U.S. dataset. Other frequently mentioned technologies include Linux at 19%, AWS at 14%, PowerShell at 14%, Azure at 13%, and Bash at 11%.
Web Security
For application-focused roles, understanding web technologies is extremely useful.
Learn how:
- Browsers communicate with servers
- Sessions and cookies work
- Authentication and authorization differ
- APIs exchange data
- Databases interact with applications
- Input reaches backend systems
- Security controls can fail
Burp Suite, JavaScript, SQL, and HTTP knowledge can become valuable parts of an application-security toolkit.
Cloud Security
Modern pentesters increasingly encounter cloud environments.
Learning AWS or Azure fundamentals can help you understand cloud identities, permissions, network configurations, storage, workloads, and security controls.
Documentation and Communication
Technical ability alone does not make a successful professional pentester.
The customer needs to understand what was discovered, why it matters, how it was demonstrated, and what should be done next.
A professional report should generally distinguish technical evidence from business impact and provide practical remediation guidance.
O*NET specifically identifies report writing, communication with IT teams and management, and recommending solutions among the responsibilities associated with the occupation.
Tools Commonly Associated With Penetration Testing
Tools vary depending on the engagement, but job-posting data provides useful insight into technologies employers mention.
| Tool or Technology | Typical Use |
|---|---|
| Python | Automation and custom scripts |
| Linux | Security testing environment and administration |
| PowerShell | Windows automation and security testing |
| Burp Suite | Web application testing |
| Nmap | Network discovery and service enumeration |
| Metasploit | Exploitation and security testing |
| Nessus | Vulnerability assessment |
| AWS | Cloud security testing |
| Azure | Cloud and identity environments |
| Active Directory | Enterprise Windows security testing |
| Kali Linux | Penetration-testing environment |
| Bash | Linux automation and scripting |
The 2025 U.S. employer-posting data tracked by O*NET lists Python, Linux, AWS, PowerShell, Azure, Nessus, Bash, Burp Suite, Metasploit, Nmap, Active Directory, and Kali Linux among technologies associated with penetration-tester postings.
The important lesson is not to memorize dozens of tools. Learn the underlying concepts first, then understand when and why a particular tool should be used.
Do You Need a Degree for Penetration Testing?
A degree can be helpful, particularly when applying to larger organizations, consulting companies, government contractors, or roles with formal education requirements.
Common degrees include:
- Cybersecurity
- Computer Science
- Information Technology
- Information Security
- Computer Engineering
- Network Engineering
However, employers may also value practical skills, certifications, labs, professional experience, and demonstrated security knowledge.
The broader information-security occupation tracked by the BLS typically lists a bachelor’s degree as the entry-level education, while individual penetration-testing vacancies can have different requirements.
For someone without a degree, building a strong practical portfolio can help demonstrate ability. Legal practice environments, capture-the-flag platforms, home labs, security projects, technical write-ups, and documented learning projects can all provide evidence of hands-on skills.
Certifications That Can Help
Certifications are not a replacement for practical ability, but they can help demonstrate structured knowledge.
CompTIA PenTest+
CompTIA’s PenTest+ certification is focused specifically on penetration testing and vulnerability-management skills.
It can be relevant to professionals who want a vendor-neutral credential covering planning, scanning, vulnerability identification, exploitation, reporting, and remediation.
Certified Ethical Hacker
The EC-Council Certified Ethical Hacker credential is another widely known certification in ethical hacking and security testing.
It focuses on understanding offensive security concepts and techniques within an authorized and ethical framework.
OSCP and OSCP+
OffSec’s OSCP is strongly focused on hands-on penetration testing.
The current OSCP+ exam includes practical testing against standalone machines and an Active Directory environment. OffSec states that the exam assesses skills including vulnerability identification, exploitation, privilege escalation, and documentation.
More advanced professionals can also consider certifications such as OSEP, which focuses on advanced offensive-security skills and complex attack scenarios.
A sensible approach is to choose certifications based on your existing experience rather than collecting credentials without developing practical skills.
What Do Penetration Testers Earn?
Salary varies considerably according to experience, location, specialization, industry, clearance requirements, and employer.
There is no single official federal salary category specifically covering every penetration tester, so broader information-security salary data should not be presented as a guaranteed pentester salary.
The BLS reports a May 2025 median annual wage of $129,180 for information security analysts. The lowest 10% earned below $75,090, while the highest 10% earned above $199,850.
Current job-board listings also demonstrate how widely advertised compensation can vary. For example, the current ZipRecruiter page includes a remote Penetration Tester listing at $102,000–$122,000 annually, an Associate Penetration Tester listing at $85,000–$102,000, and a Senior Penetration Tester listing at $90,000–$150,000.
ClearanceJobs currently shows additional examples, including penetration-testing positions advertising ranges such as $102,000–$122,400 and $113,200–$237,800, although these figures are associated with specific roles, locations, clearance requirements, and employers rather than the entire profession.
| Career Level | Example Current Advertised Range | Important Consideration |
|---|---|---|
| Associate/Junior | $65K–$102K+ | Experience and technical foundation matter |
| Penetration Tester | $86K–$150K+ | Location and specialization can affect pay |
| Senior Penetration Tester | $90K–$198K+ | Advanced skills and experience often required |
| Specialized/Cleared Roles | $100K–$237K+ in some listings | Clearance and role requirements can significantly affect compensation |
These are examples from current job advertisements, not standardized salary bands. Actual compensation can differ substantially.
Remote Penetration Testing Opportunities
Remote work is one of the notable features of the current penetration-testing market.
Current ZipRecruiter listings include remote penetration-testing positions as well as hybrid roles. The listings cover organizations seeking penetration testers, offensive-security consultants, associate testers, external network testers, and senior specialists.
Remote work can be especially practical for consulting-oriented assessments because much of the technical testing can be conducted through secure remote environments.
However, “remote” does not always mean fully location-independent. Some positions may require occasional travel, work within particular states, or access to customer facilities.
Candidates should therefore read the location and travel requirements carefully before applying.
Government and Security-Cleared Penetration Testing Roles
Government contractors represent another important segment of the market.
ClearanceJobs currently displays more than 100 listings under its penetration-tester search, including roles requiring Secret, Top Secret, and TS/SCI clearances. Some positions also list polygraph requirements.
These jobs can involve:
- Defense networks
- Federal agencies
- National-security systems
- Government applications
- Enterprise infrastructure
- Classified environments
- Security assessments
For example, current listings include penetration-testing positions at organizations such as Booz Allen Hamilton, CACI, Kratos, GovCIO, Goldbelt, and other contractors. Several listings specify clearance requirements and experience levels.
Candidates interested in this sector should carefully review clearance eligibility and job-specific requirements because security-cleared positions can have requirements that do not appear in commercial cybersecurity jobs.
How to Build Experience Before Your First Job
One of the biggest challenges for newcomers is gaining practical experience.
You can start by creating a controlled cybersecurity laboratory where you own or have explicit permission to test the systems.
Build a Home Lab
A basic lab can include virtual machines running different operating systems.
You can practice:
- Network enumeration
- Service identification
- Vulnerability analysis
- Web application testing
- Linux administration
- Windows security
- Active Directory fundamentals
- Basic scripting
Never test systems that you do not own or have explicit authorization to assess.
NIST’s SP 800-115 provides guidance for organizations planning and conducting technical security testing and assessment, including testing methods, analysis, and mitigation planning.
Practice With Legal Training Environments
Purpose-built security labs provide a safer way to develop offensive-security skills.
Practice environments allow you to experiment with vulnerabilities without attacking real organizations or unauthorized systems.
Keep notes about what you learn and document the methodology, evidence, and remediation for each exercise.
Create a Portfolio
A portfolio can demonstrate practical ability beyond a list of certifications.
Useful projects might include:
- A home Active Directory lab
- A web application security assessment
- A network security assessment
- A Python security-automation project
- A vulnerability-analysis report
- A cloud-security laboratory
- A documented CTF challenge
Avoid publishing sensitive information or real-world exploit details from systems you are not authorized to test.
How to Apply for Your First Role
Searching for the exact phrase “penetration tester” is useful, but it should not be your only strategy.
Employers may advertise related positions using titles such as:
- Security Consultant
- Security Engineer
- Vulnerability Assessor
- Offensive Security Consultant
- Ethical Hacker
- Application Security Tester
- Red Team Operator
- Security Assessment Analyst
- Cybersecurity Consultant
O*NET lists several related job titles associated with the penetration-testing occupation, including Security Consultant, Security Engineer, System Vulnerability Analyst, Threat Hunter, and Vulnerability Assessor.
When reading a job description, look beyond the title. Compare the required technologies, years of experience, certifications, clearance requirements, testing methodologies, and reporting responsibilities.
A Practical 12-Month Learning Roadmap
If you are starting from the beginning, a structured approach can make the learning process easier.
| Period | Main Goal | What to Learn |
|---|---|---|
| Months 1–2 | IT foundation | Networking, TCP/IP, DNS, Linux, Windows |
| Months 3–4 | Security foundation | Authentication, vulnerabilities, security controls |
| Months 5–6 | Pentesting fundamentals | Reconnaissance, scanning, enumeration, reporting |
| Months 7–8 | Web security | HTTP, APIs, authentication, Burp Suite |
| Months 9–10 | Enterprise security | Active Directory, PowerShell, Windows environments |
| Month 11 | Portfolio | Labs, reports, practical security projects |
| Month 12 | Job preparation | Resume, interviews, certification, applications |
The timeline is only a framework. Someone with an IT background may progress faster in some areas, while a complete beginner may need additional time.
Common Mistakes to Avoid
Learning Tools Without Understanding Technology
Knowing how to run Nmap or another security tool is not the same as understanding the network being tested.
Focus on concepts first.
Ignoring Reporting
A tester who discovers a serious vulnerability but cannot explain it clearly has not completed the job effectively.
Practice writing concise findings that explain the vulnerability, evidence, impact, and recommended remediation.
Collecting Too Many Certifications
Certifications can help, but practical skills matter too.
It is generally more useful to understand one area deeply than to collect credentials without hands-on experience.
Testing Unauthorized Systems
Only perform penetration testing when you have explicit permission and a clearly defined scope.
Professional security testing depends on authorization, rules of engagement, responsible handling of information, and controlled execution.
Where to Find Penetration Testing Opportunities
Job seekers can monitor several types of platforms.
General job boards: Search for penetration tester, ethical hacker, offensive security, security consultant, and vulnerability-assessment roles.
Specialized cybersecurity boards: These can be useful for finding security-focused positions.
Government and cleared-job boards: Platforms such as ClearanceJobs are particularly relevant for candidates pursuing federal and defense-related cybersecurity work. Its current listings demonstrate opportunities across different experience levels, clearance categories, and work arrangements.
Company career pages: Security consulting companies, defense contractors, technology companies, financial institutions, and cloud-focused businesses may advertise offensive-security positions directly.
Final Thoughts
A career in penetration testing combines technical knowledge, curiosity, structured problem-solving, and communication. The field includes entry-level, network, web application, cloud, red team, consulting, and senior roles, so there is more than one way to build a career.
Current labor-market data shows strong growth across the broader information-security profession, while current job listings demonstrate demand for penetration testers across commercial, remote, consulting, and government environments.
If you are starting from scratch, focus first on networking, operating systems, scripting, web technologies, and security fundamentals. Then build hands-on experience through authorized labs, create a practical portfolio, consider a relevant certification, and apply for roles whose requirements match your developing skills.
The most valuable preparation is not simply learning how to use hacking tools. It is learning how to think like an attacker while working responsibly like a security professional. That combination can help you pursue Pen Testing Jobs and related offensive-security careers as your experience grows.

Read Dive is a leading technology blog focusing on different domains like Blockchain, AI, Chatbot, Fintech, Health Tech, Software Development and Testing. For guest blogging, please feel free to contact at readdive@gmail.com.